Traditional network security approaches historically operated on the assumption that anything already inside an organisation’s network perimeter could be trusted, yet this assumption has proven increasingly problematic as businesses navigate more complex, distributed technology environments. Zero trust architecture specifically challenges this traditional assumption, and what this security approach actually involves, and why businesses are adopting it with increasing urgency, provides important context for modern cybersecurity strategy.
What Zero Trust Architecture Actually Means
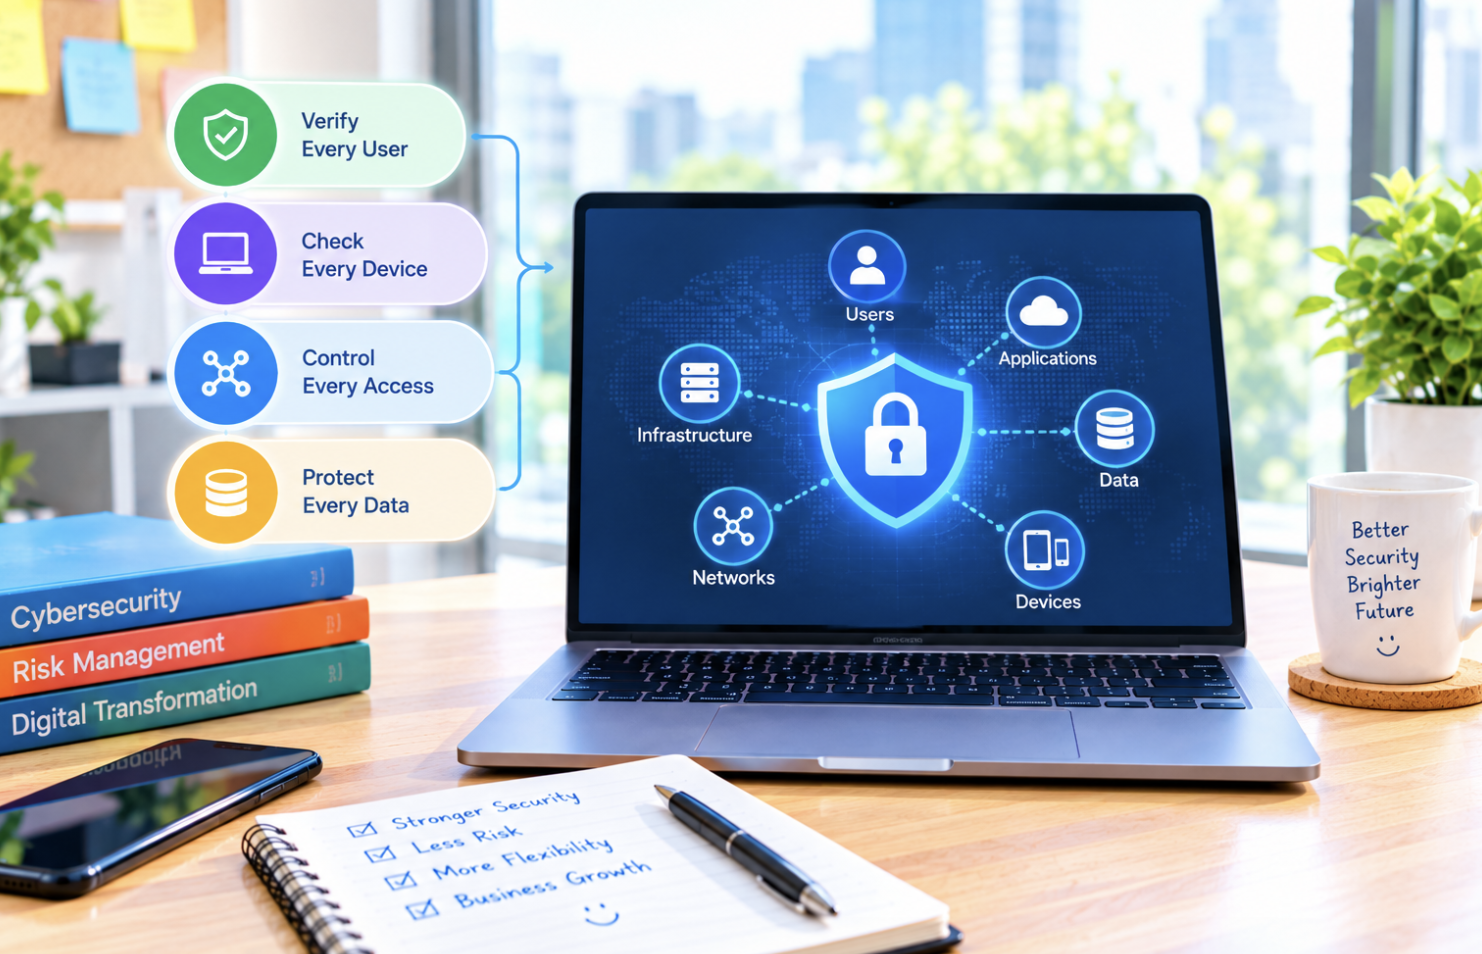
Zero trust architecture is a security approach based on the fundamental principle that no user or device should be automatically trusted, regardless of whether they exist inside or outside an organisation’s traditional network perimeter. This represents a significant departure from traditional security models, which typically granted considerable trust to anything already operating within the internal network, instead requiring, continuous verification for every access request regardless of its apparent origin.
This “never trust, always verify” principle matters, since it addresses a fundamental vulnerability within traditional security approaches, given that once an attacker gained access to a traditionally trusted internal network, they could often move relatively freely without facing the kind of continuous verification zero trust architecture specifically requires at every subsequent step.
Why Traditional Perimeter-Based Security Became Insufficient
The specific, reasons traditional network perimeter security approaches have become increasingly inadequate helps clarify why zero trust architecture has gained such significant, urgent business attention.
- Modern businesses increasingly operate with distributed employees, devices, and cloud-based resources
- This distribution means a traditional, clearly defined network perimeter no longer adequately represents reality
- Attackers who successfully breach traditional perimeter defences could historically move with limited additional resistance
- These changes helps clarify why the traditional trusted internal network assumption has become problematic
This perimeter dissolution deserves particular emphasis, since the traditional concept of a clearly defined, protected internal network made more practical sense when employees worked from company-owned devices within physical office locations connecting to on-premises systems, while contemporary work increasingly involves distributed employees using various devices, connecting to cloud-based resources from various locations, meaning the traditional, clearly defined perimeter this security model depended upon has become considerably less meaningful as a practical security boundary.
The Core Principles Underlying Zero Trust Architecture
The specific, foundational principles that comprise zero trust architecture helps clarify how this security approach actually translates into practical implementation.
- Every access request requires verification, regardless of the requester’s apparent location or network origin
- Access permissions follow the principle of least privilege, providing only necessary access
- Continuous monitoring helps detect and respond to suspicious activity throughout ongoing sessions, not just initial access
- These combined principles helps clarify zero trust architecture’s comprehensive security approach
This least privilege principle deserves particular emphasis, since zero trust architecture specifically avoids granting broad, general access simply because a user has been authenticated, instead ensuring that authenticated users receive only the specific access actually necessary for their particular role or task, meaning even a successfully compromised account provides an attacker considerably more limited access compared to traditional security models that might grant broader access following successful initial authentication alone.
How Zero Trust Architecture Addresses Modern Threat Patterns
How zero trust architecture specifically addresses, contemporary threat patterns that traditional security approaches struggle to adequately handle helps clarify this approach’s particular practical relevance.
- Zero trust architecture limits the potential damage from compromised credentials or insider threats
- Continuous verification helps detect unusual activity patterns that might indicate compromise
- This approach reduces the practical value attackers gain from breaching any single access point
- This threat-focused design helps clarify zero trust’s relevance to contemporary security challenges
The Practical Components of Zero Trust Implementation
The specific, technical and organisational components that typically comprise practical zero trust architecture implementation helps clarify how this security philosophy actually translates into concrete business practice.
- Strong identity verification, often including multi-factor authentication, forms a foundational component
- Network segmentation helps limit how far any potential compromise could spread
- Comprehensive monitoring and logging provides visibility into access patterns and potential anomalies
- These components helps clarify the multifaceted technical work zero trust implementation actually involves
This monitoring visibility deserves particular emphasis, since zero trust architecture’s continuous verification principle depends on having comprehensive, ongoing visibility into how users and systems actually behave throughout their sessions, not simply during initial authentication, meaning organisations need robust monitoring and logging capabilities to actually detect the kind of suspicious activity patterns that would indicate a security concern requiring intervention under this security model.
The Business Motivations Driving Zero Trust Adoption
The specific, business factors motivating organisations to actually adopt zero trust architecture helps clarify why this approach has moved from theoretical security concept toward increasingly common practical implementation.
- Growing remote and hybrid work arrangements have increased the practical relevance of this security approach
- Increasing cloud service adoption has reduced the practical meaning of traditional network perimeters
- Rising awareness of sophisticated cyberattack methods has motivated more comprehensive security approaches
- These business drivers helps clarify zero trust’s, growing relevance for contemporary organisations
The Implementation Challenges Organisations Commonly Face
The real, challenges organisations commonly encounter when actually implementing zero trust architecture helps provide honest, balanced context beyond simply theoretical security benefits alone.
- Implementing comprehensive zero trust architecture requires significant organisational and technical investment
- Existing legacy systems sometimes present integration challenges within a zero trust framework
- Organisational culture and workflow changes accompany this significant security philosophy shift
- These challenges helps set realistic expectations for organisations considering zero trust adoption
Why Zero Trust Represents an Ongoing Journey Rather Than a Single Achievement
Zero trust architecture represents an ongoing organisational journey rather than a single, completed implementation milestone helps clarify realistic expectations for this significant security transformation.
- Organisations typically implement zero trust principles gradually, rather than through immediate, complete transformation
- This gradual approach allows manageable implementation while progressively strengthening overall security posture
- Continued refinement and adaptation remains necessary as organisational needs and threats continue evolving
- This ongoing nature helps organisations approach zero trust adoption with realistic, sustainable expectations
How Zero Trust Architecture Addresses Third-Party and Vendor Access
How zero trust principles extend to managing third-party vendor and contractor access helps clarify an important, often overlooked application of this security philosophy beyond simply internal employee access alone.
- Organisations increasingly grant various external parties some level of system access for legitimate business needs
- Zero trust principles apply equally to this external access, requiring the same rigorous, continuous verification
- This consistent approach helps address security risks that third-party access has historically sometimes introduced
- This application helps clarify zero trust’s comprehensive scope beyond simply internal organisational boundaries
The Role of Automation in Practical Zero Trust Implementation
Why automation plays an essential role in making comprehensive zero trust architecture practically manageable helps clarify an important technical consideration for organisations pursuing this security approach.
- Manually managing the continuous verification zero trust requires would prove impractical at meaningful scale
- Automated systems handle much of the ongoing verification and monitoring this security model actually requires
- This automation allows organisations to implement zero trust principles without overwhelming security staff resources
- This automation dependency helps clarify why appropriate technical tooling matters significantly for zero trust success
Final Thoughts
Zero trust architecture fundamentally challenges traditional security assumptions by requiring continuous verification for every access request regardless of apparent origin, addressing vulnerabilities that traditional perimeter-based security approaches struggle to handle within increasingly distributed, cloud-based modern business environments. This security philosophy’s principles and the practical, honest challenges organisations face during implementation provides valuable context for why businesses increasingly view zero trust adoption as essential for navigating contemporary cybersecurity challenges.
Frequently Asked Questions
1. Is zero trust architecture only relevant for large enterprise organisations?
No, while large organisations often have more extensive resources for comprehensive implementation, zero trust principles can benefit organisations of various sizes, with smaller organisations often able to implement core principles more quickly given their comparatively simpler existing infrastructure.
2. Does implementing zero trust architecture eliminate all cybersecurity risk?
No, no security approach provides complete, absolute protection, meaning zero trust architecture should be understood as significantly strengthening an organisation’s security posture rather than providing guaranteed, complete immunity from all possible security incidents.
3. How long does comprehensive zero trust implementation typically take for organisations?
This varies considerably based on organisational size and existing infrastructure complexity, though comprehensive implementation often takes considerable time, sometimes spanning years for larger, more complex organisations pursuing genuinely thorough transformation across their entire technology environment.
4. Does zero trust architecture make everyday work more difficult for employees?
Well-implemented zero trust architecture aims to balance security with usability, though some additional verification steps compared to traditional approaches are inherent to this model, making thoughtful implementation important for maintaining reasonable employee experience alongside improved security.
5. Can zero trust architecture be implemented gradually, rather than requiring complete organisational transformation immediately?
Yes, most organisations successfully pursuing zero trust adoption do so through gradual, phased implementation, progressively strengthening specific areas rather than attempting immediate, comprehensive transformation across their entire technology environment simultaneously.
6. Is zero trust architecture considered current cybersecurity best practice?
Yes, zero trust architecture has become widely recognised among cybersecurity professionals and organisations as an important, recommended approach for addressing contemporary security challenges, reflecting significant, broad consensus regarding its practical value and relevance.